
Oracle E-Business Suite (EBS) remains the backbone of critical business operations, including finance, procurement, supply chain management, and human resources. Because Oracle EBS stores sensitive business data and supports key transactions, security weaknesses can expose organizations to compliance violations, operational disruptions, data breaches, and financial risks.
Many organizations believe that applying Oracle patches or conducting occasional audits is enough to stay secure. However, modern Oracle EBS environments often include customizations, third-party integrations, cloud infrastructure, remote access requirements, and complex user roles that introduce new security challenges.
As a result, businesses need a comprehensive Oracle EBS Security Assessment to identify vulnerabilities, validate security controls, and reduce risk before issues impact operations. The effectiveness of the assessment largely depends on the service provider you choose. A qualified provider should go beyond a simple checklist and deliver actionable insights, risk-based recommendations, compliance guidance, and a practical remediation roadmap.
In this article, we’ll discuss what organizations should expect from Oracle EBS Security Assessment Services and how to evaluate the right partner for long-term security resilience.
What Is an Oracle EBS Security Assessment?
An Oracle EBS Security Assessment is a structured review of the application’s security posture, including users, responsibilities, configurations, database settings, integrations, infrastructure components, and compliance controls.
Unlike a standard vulnerability scan, a comprehensive Oracle EBS Security Review focuses on business risks as well as technical weaknesses.
The assessment should answer questions such as:
- Do users have appropriate access?
- Are SoD conflicts creating compliance risks?
- Are security configurations aligned with best practices?
- Are Oracle security patches current?
- Are integrations introducing vulnerabilities?
- Are security controls sufficient for regulatory requirements?
The goal is not simply to find problems. The goal is to provide organizations with a practical roadmap for reducing risk and improving security maturity.
Why Oracle EBS Security Assessments Have Become a Business Priority
Oracle EBS is no longer isolated within the corporate network. Most environments interact with third-party applications, reporting tools, cloud platforms, partner systems, and remote users.
As a result, organizations face growing concerns such as:
- Unauthorized access to sensitive transactions
- Privileged account misuse
- Compliance violations
- Data exposure risks
- Inadequate monitoring controls
- Increasing cyber threats targeting enterprise applications
A security assessment helps organizations proactively identify these risks before they lead to financial, operational, or reputational damage.
Some of the most common reasons businesses initiate an Oracle EBS Security Assessment include:
- Preparing for compliance or internal audits
- Planning an Oracle Cloud Infrastructure (OCI) migration
- Recovering from security incidents
- Evaluating user access controls
- Reviewing security after Oracle EBS upgrades
- Strengthening cyber resilience initiatives
Rather than responding to security issues after they occur, organizations can use assessments to create a proactive security improvement strategy.
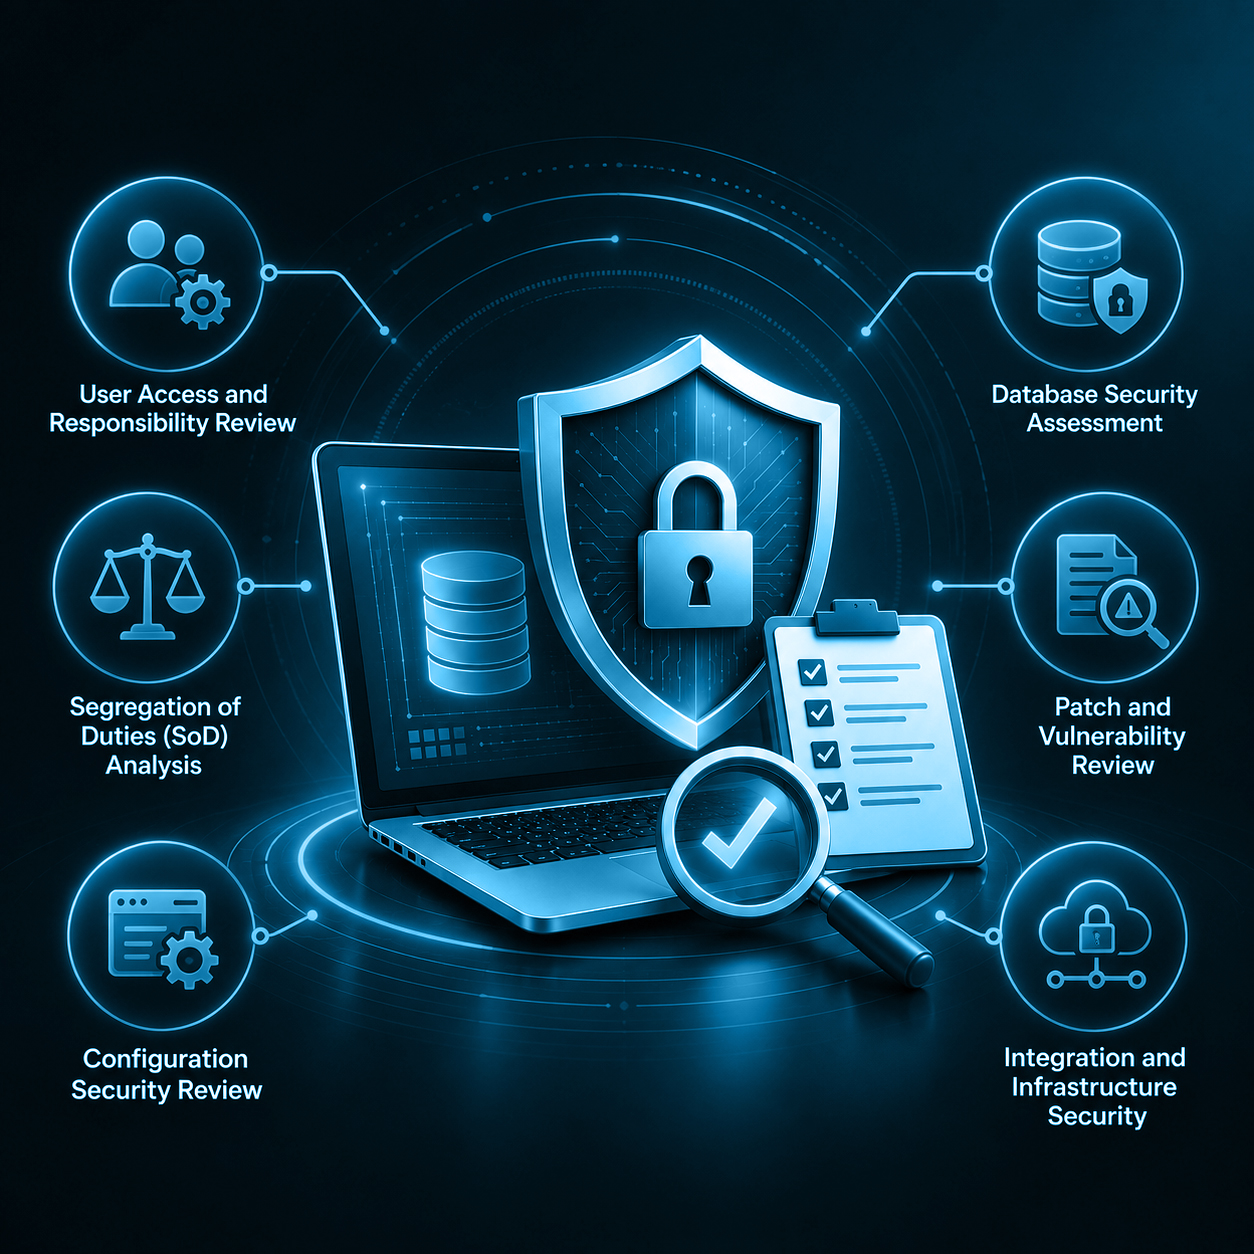
Oracle EBS Security Assessment Checklist: What a Service Provider Should Evaluate
One of the biggest differences between average and high-quality Oracle EBS Security Assessment Services is the depth of the review.
A qualified provider should evaluate the entire Oracle ecosystem rather than focusing on a single component.
1. User Access and Responsibility Review
User access remains one of the most common sources of Oracle EBS security findings.
Over time, employees change roles, contractors leave, projects end, and business requirements evolve. Unfortunately, access permissions often remain untouched.
A thorough review should examine:
- Dormant users
- Shared accounts
- Generic accounts
- Privileged access
- Sensitive responsibilities
- Access approval processes
The objective is to verify that users only have access necessary to perform their current business functions.
2. Segregation of Duties (SoD) Analysis
SoD conflicts represent a significant risk within Oracle EBS environments.
For example, if a user can create a supplier, enter invoices, and approve payments, the organization may face increased fraud and compliance risks.
A comprehensive assessment should:
- Identify SoD conflicts
- Classify risks by severity
- Recommend mitigation controls
- Validate existing compensating controls
This area is especially important for organizations subject to SOX or internal governance requirements.
3. Configuration Security Review
Oracle EBS security depends heavily on configuration settings.
Even a fully patched environment can remain vulnerable if security controls are not configured appropriately.
Typical review areas include:
- Password policies
- Authentication controls
- Session settings
- Profile options
- Approval workflows
- Audit configurations
Providers should evaluate whether these settings align with Oracle EBS security best practices and organizational security requirements.
4. Database Security Assessment
Application security is not enough. Many Oracle EBS security issues originate within the database layer, making database security a critical part of any Oracle EBS Vulnerability Assessment.
The review should include:
- User privileges
- Administrative access
- Public grants
- Default accounts
- Audit settings
- Database hardening controls
Organizations frequently find hidden risks during database reviews that would not be identified through application-level analysis alone.
5. Patch and Vulnerability Review
Oracle regularly releases Critical Patch Updates (CPUs) to address newly identified vulnerabilities.
An effective assessment should evaluate:
- Current patch levels
- Missing security updates
- Patch governance processes
- Security-related patch delays
- Known vulnerability exposure
This review helps organizations understand whether patch management practices adequately protect the Oracle environment.
For organizations making frequent changes to Oracle applications, combining security reviews with Oracle Testing Services can help validate changes while reducing operational risk.
6. Integration and Infrastructure Security
Modern Oracle EBS environments rarely operate independently.
They often connect with:
- ERP extensions
- Banking systems
- Reporting tools
- Identity management solutions
- Cloud platforms
- Third-party applications
Each integration introduces potential security considerations.
A qualified provider should evaluate both application-level and infrastructure-level controls to identify gaps that may create unnecessary exposure.
Oracle EBS Compliance Assessment Requirements
Compliance is often one of the primary reasons organizations engage Oracle EBS Security Consulting Services.
A strong Oracle EBS Compliance Assessment should evaluate alignment with requirements such as:
- SOX
- GDPR
- PCI DSS
- Internal governance frameworks
Security controls that cannot be demonstrated to auditors can become compliance findings, regardless of how effective they appear on paper.
In addition to identifying gaps, the provider should help answer three critical questions:
- Are Security Controls Properly Designed? The assessment should determine whether access controls, monitoring processes, and security configurations adequately address identified risks.
- Are Controls Operating Effectively? Controls that exist but are not routinely monitored often provide limited protection.
- Can Audit Evidence Be Produced? Organizations should be able to demonstrate compliance through audit trails, approval of histories, access reviews, and security documentation.
Not Sure Where Your Security Risks Exist?
A professional Oracle EBS Security Assessment can uncover hidden access risks, SoD conflicts, compliance gaps, and configuration weaknesses before they become audit findings or operational issues.
Winfo Solutions helps organizations evaluate Oracle EBS, database, infrastructure, and OCI security controls, providing a prioritized remediation roadmap aligned to business risk.
Not Sure Where Your Security Risks Exist?
A professional Oracle EBS Security Assessment can uncover hidden access risks, SoD conflicts, compliance gaps, and configuration weaknesses before they become audit findings or operational issues. Winfo Solutions helps organizations evaluate Oracle EBS, database, infrastructure, and OCI security controls, providing a prioritized remediation roadmap aligned to business risk.
What Deliverables Should You Expect from Oracle EBS Security Consulting Services?
One common frustration among organizations is receiving a lengthy report with little guidance on the next steps.
A mature Oracle EBS Security Assessment should provide actionable deliverables tailored to both executive and technical audiences.
Executive-Level Deliverables
Leadership teams typically need:
- Risk summary
- Business impact assessment
- Compliance exposure overview
- Prioritized recommendations
- Strategic roadmap
Technical Deliverables
Oracle administrators and security teams require:
- Detailed findings
- User access analysis
- Configuration review results
- Database assessment findings
- Patch management observations
- Remediation recommendations
Remediation Roadmap
Perhaps the most valuable deliverable is a remediation plan that helps teams understand:
- What should be fixed immediately
- What requires short-term attention
- Which improvements should be planned strategically
- How risks can be reduced over time
Without a remediation roadmap, assessment findings often fail to translate into meaningful improvements.
How Oracle EBS Assessments Differ Across On-Premises, OCI, and Hybrid Environments
Security requirements vary significantly depending on deployment architecture.
Area of Focus | On-Premises | OCI | Hybrid |
Infrastructure Controls | High | Moderate | High |
IAM Security | Moderate | High | High |
Cloud Governance | Low | High | High |
Network Security | High | High | High |
Integration Complexity | Moderate | Moderate | High |
On-Premises Environments
Organizations must focus heavily on infrastructure protection, network segmentation, server hardening, and patch management practices.
Oracle Cloud Infrastructure (OCI)
OCI introduces additional areas that should be assessed, including:
- Identity and Access Management (IAM)
- Network security architecture
- Cloud governance
- Data protection controls
- Storage security
Organizations considering cloud migration should align security assessments with broader transformation initiatives.
This is where WinfoCloudX Transformation Services can help organizations evaluate Oracle workloads, identify migration risks, and improve cloud readiness.
Hybrid Deployments
Hybrid environments often present the greatest complexity because security controls must remain consistent across both on-premises and cloud resources.
What We Commonly See During Oracle EBS Security Assessments
Every Oracle environment is different, but certain findings appear repeatedly across industries.
Our Oracle EBS security specialists frequently identify:
- Responsibilities that were never removed after employee role changes
- Privileged access granted without ongoing review
- Security configurations that no longer align with current business needs
- Legacy integrations that introduce unnecessary risk exposure
- Audit controls that exist but are not consistently monitored
These findings are often not the result of negligence. Most develop gradually as Oracle environments evolve through upgrades, customizations, acquisitions, and changing business processes.
This is why periodic Oracle EBS Security Assessments remain essential, even for organizations with mature IT teams and established governance frameworks.
Questions to Ask Before Choosing an Oracle EBS Security Assessment Provider
Selecting the right provider is just as important as conducting the assessment itself.
Before engaging with a partner, organizations should evaluate the provider’s Oracle expertise and practical experience.
Consider asking:
About Oracle Expertise
- Do you specialize in Oracle EBS?
- Have you assessed environments similar to ours?
- Can you review both application and database security?
About Assessment Methodology
- How do you identify business risks?
- Do you perform SoD analysis?
- How are findings prioritized?
About Post-Assessment Support
- Do you assist with remediation?
- Can you help with compliance initiatives?
- Do you support OCI transformation projects
The answers often reveal whether the provider delivers practical business value or only technical observations.
Red Flags That Indicate a Weak Oracle EBS Security Assessment
Not all assessments are created equal.
Be cautious if the provider:
- Relies only on automated scanning tools
- Lacks Oracle EBS-specific expertise
- Does not assess SoD conflicts
- Ignores database security
- Provides generic recommendations
- Delivers no remediation roadmap
- Offers limited executive reporting
A meaningful Oracle EBS Security Assessment should combine technical expertise, risk management knowledge, compliance understanding, and Oracle-specific experience.
How Winfo Solutions Helps Strengthen Oracle EBS Security
At Winfo Solutions, we understand that security assessments should lead to measurable outcomes, not just reports.
Our Oracle EBS Security Assessment Services help organizations identify risks across their Oracle environments and prioritize remediation based on business impact.
Our assessment approach focuses on three stages:
Assess
We evaluate:
- User access controls
- SoD risks
- Oracle EBS configurations
- Database security
- Infrastructure controls
- Compliance requirements
Prioritize
Findings are ranked according to business risk, helping organizations focus resources where they matter most.
Improve
Organizations receive practical recommendations that support:
- Security improvement initiatives
- Compliance readiness
- OCI transformation planning
- Cyber resilience strategies
- Long-term Oracle governance
For customers planning modernization initiatives, our security assessments can also align with WinfoCloudX transformation programs and WinfoTest automation capabilities to support secure and stable Oracle operations.
Moving From Security Assessments to Continuous Improvement
An Oracle EBS security assessment provides a point-in-time view of vulnerabilities, configuration gaps, excessive access, and other security risks. The real value comes from how those findings are addressed and monitored over time.
Organizations should use assessment results to prioritize remediation based on risk, assign ownership for identified issues, and establish regular reviews of user access, security configurations, patches, and privileged accounts. Significant application changes should also be tested to confirm that security improvements do not affect critical Oracle EBS processes.
Security planning should also consider operational resilience. For business-critical Oracle EBS environments, this can include reviewing backup and recovery procedures, disaster recovery readiness, and the ability to restore essential business processes following an outage or security incident.
As the Oracle environment changes through upgrades, integrations, cloud initiatives, or new business requirements, security controls should be reviewed again rather than relying on the results of a one-time assessment.
Conclusion
Oracle EBS security is not a one-time project. As users change roles, integrations expand, business processes evolve, and cloud initiatives accelerate, new risks emerge that can impact compliance, operational stability, and business continuity.
A comprehensive Oracle EBS Security Assessment helps organizations identify hidden vulnerabilities, eliminate unnecessary risk exposure, improve audit readiness, and establish a stronger foundation for future growth.
Whether you are preparing for an audit, planning an OCI migration, reviewing user access controls, or strengthening your cybersecurity strategy, partnering with an experienced Oracle security provider can make the difference between simply identifying risks and successfully resolving them.
At Winfo Solutions, we help organizations assess, prioritize, and remediate Oracle EBS security risks through a structured, business-focused approach designed to support long-term security resilience and operational success.
Ready to evaluate the security of your Oracle EBS environment?
Contact Winfo Solutions to discuss your Oracle EBS Security Assessment requirements and receive expert guidance tailored to your Oracle ecosystem, compliance needs, and transformation goals.
FAQ's About Oracle EBS Security Assessment Services
1. What is included in Oracle EBS Security Assessment Services?
Most assessments include user access reviews, SoD analysis, configuration reviews, database security assessments, patch evaluations, integration reviews, compliance checks, and remediation recommendations.
2. How often should an Oracle EBS Security Assessment be performed?
Organizations typically benefit from annual assessments or assessments conducted before audits, cloud migrations, major upgrades, or security initiatives.
3. What is the difference between an Oracle EBS Security Audit and a Security Assessment?
A security audit primarily validates compliance requirements, while a security assessment identifies risks and recommends improvements.
4. Is an Oracle EBS Security Assessment necessary before migrating to OCI?
Yes. Conducting an assessment before migration helps identify existing vulnerabilities and prevents security issues from being carried into the cloud environment.